🔍 Read the full analysis: What’s Behind The Rise In CVEs? The Data On AI And Bug Hunters on ThorstenMeyerAI.com

Get hardware and tech essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
An analysis of NVD and CVE.org records found 13,934 new CVE records published from Oct. 1 through Oct. 25, 2026—3.2 times the total for all of October 2025. The records show a sharp increase in disclosures but do not establish how much AI contributed to finding bugs; the analysis also reports that only 516 of 6,157 vulnerabilities Anthropic says it reported to maintainers are known to be patched.
A new analysis of public vulnerability records found 13,934 CVE records published from Oct. 1 through Oct. 25, 2026, compared with 4,389 across all of October 2025, while concluding that the data does not show how much artificial intelligence contributed to finding the bugs. The findings matter because the growing disclosure count is not the same as a count of newly exploited flaws—and the analysis points to a substantial gap between reported vulnerabilities and known patches.
Thorsten Meyer’s analysis, published Oct. 26, says it queried the U.S. National Vulnerability Database API for publication dates from January 2022 onward and cross-checked October records against CVE.org. The two sources agreed on 13,766 October records and 202 records later rejected; the analysis’s total of 13,934 for Oct. 1–25 includes the published records it counted for that period. It reports 88,772 CVEs so far in 2026, which it compares with 2025’s full-year total of 49,973.
The monthly figures show a rapid rise: 8,001 records in June, 9,919 in July, 12,719 in August and 15,074 in September. The analysis says the daily rate increased 20% from June to July, 28% from July to August and 22% from August to September; the comparable increase for October to date was about 11%. Meyer projects that October could finish near 17,000 records if the pace continues, but that figure is a projection, not a final count.
The increase is concentrated among several large organizations and numbering bodies. Microsoft’s October count rose from 180 records in October 2025 to 1,455 this October; Oracle’s rose from 78 to 1,078, and GitHub’s from 276 to 1,159. The analysis says Microsoft’s Oct. 2026 total includes a Patch Tuesday release covering 1,413 CVEs, citing SecurityWeek. These counts describe published records, not necessarily separate incidents or newly discovered vulnerabilities.
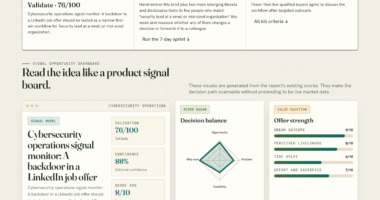
Infographic 01 · How big the CVE wave really is
The CVE chart is real. Steep, not parabolic.
New vulnerability records have tripled year over year. A handful of big vendors and clearinghouses drive the jump, and the growth rate cooled in October.
New CVE records per month
January 2024 – 25 October 2026 · phones show the last 13 months
Growth of new CVEs per day versus the previous month. Steep, but the acceleration slowed in October: not “parabolic”.
Who publishes the jump
records by CVE Numbering Authority, October vs. October
Microsoft’s October Patch Tuesday fixed a record 1,413 CVEs (SecurityWeek (14 Oct 2026)). The Linux kernel grew far less.
Not a backlog dump
checks on the October 2026 records
- 98% carry a 2026 ID
- 15 days median from reserving an ID to publishing it
- 217 numbering authorities published, vs. 163 in Oct 2025
- 202 records were later rejected (counted, as NVD does)
- ~17,000 if October’s pace holds: a projection, not a count
Sources: NVD CVE API 2.0 (counts by publication date, all statuses, queried 26 Oct 2026); CVE.org records (credits field, fetched 26 Oct 2026); SecurityWeek (14 Oct 2026). Own analysis; raw files and queries in the kit.
Powered by Thorsten Meyer AI
Disclosures Outpace Known Patches
The main practical concern raised by the analysis is whether software maintainers can fix and distribute patches at the pace vulnerabilities are being reported. Anthropic’s dashboard, as summarized by Meyer, lists 6,157 vulnerabilities reported to maintainers and says 516 were patched to the company’s knowledge—about one in twelve. That figure is limited to Anthropic’s reported set and its knowledge; it is not a measure of the global patch rate.
A higher CVE count alone does not establish that attackers are exploiting more bugs. CVEs are public records of disclosed vulnerabilities, and the analysis notes that the record is generally created through a coordinated process involving vendors or other CVE Numbering Authorities. It also says CISA’s Known Exploited Vulnerabilities catalog grew by 245 entries in all of 2025, far less than the increase in CVE disclosures. The cited material does not provide a comparable 2026 total here, so the figures should not be treated as a direct, current comparison of attacker activity.
For readers and organizations responsible for software, the distinction affects how to interpret the headlines: more disclosures can help defenders identify and address flaws, but they do not show whether fixes have reached affected systems. The patch figures cited by Meyer underscore that finding and reporting a vulnerability is only one stage of reducing exposure.
Products Worth Considering

LG 34GX90SA-W 34-inch Ultragear WQHD OLED Curved Gaming Monitor

Apple MacBook Pro 14-inch with M5 Max Chip (18-Core CPU, 20-Core GPU), 48GB RAM, 2TB SSD, Space Black

Ledger Flex Crypto Wallet with 2.8-Inch E Ink Touchscreen
As an affiliate, we earn on qualifying purchases.
What CVE Records Can Show
A CVE record gives a disclosed vulnerability a shared identifier and describes information about it. It is not, by itself, a record of an attack, proof that a vulnerability is being exploited, or a definitive account of who first found it. Meyer says the records are commonly published by a CVE Numbering Authority, often a vendor, after a fix or a disclosure deadline. Criminals who find flaws do not file CVEs; when a vulnerability is discovered through exploitation, its public record may instead document the defenders’ response.
The analysis counted records by publication date and says 98% of October’s records carry a 2026 ID, with a median 15 days between ID reservation and publication. Those details led Meyer to argue the rise is not mainly a release of old records. Even so, counts can be shaped by how organizations assign and publish records. The concentration in Microsoft, Oracle, GitHub and VulnCheck means the overall curve does not represent an even increase across every software project.
AI’s role has drawn attention as labs and security firms report using models to discover software flaws. Anthropic’s dashboard, as reported in the analysis, lists 29,439 candidate vulnerabilities found by Claude models. External firms reviewed 6,123 and confirmed 92.7% as real, while 6,157 were reported to maintainers. The analysis says those findings correspond so far to 219 CVE records and 365 GitHub advisories. OpenAI’s Patch the Planet program with Trail of Bits reports “hundreds of security issues” across 19 open-source projects, each reviewed by hand.
““That is a floor, not an estimate.””
— Thorsten Meyer, summarizing the CVE.org records
The CVE records do not establish how many vulnerabilities were found with AI. Of the 13,934 October records examined, the analysis says 6,346, or 46%, name a finder. It found 200 records—1.4% of the total—that explicitly credited an AI lab or security firm, including Anthropic or Claude in 123, AI security startups in 65, and OpenAI in 16. Because more than half the records do not name a finder, the 1.4% is an explicit-credit count, not a reliable estimate of AI’s actual contribution.
The analysis also cannot establish from CVE records alone how many reported vulnerabilities are being exploited, how quickly fixes are reaching users, or whether a rising disclosure total reflects more bugs being found, changes in reporting practices, or both. Its October count covers records retrieved on Oct. 26, and the month was not complete. Meyer’s estimate of a roughly 17,000-record October is conditional on the pace holding and remains unconfirmed.
The supplied material refers to claims that attackers are using inexpensive AI agents against older vulnerabilities and that an open-weight model can build exploits with weak safeguards. Those claims are attributed in the source to NorForge, Reuters and Anthropic, but the material does not provide enough supporting detail to independently establish their scale or effects. The cited CISA total covers 2025, not the full 2026 period under discussion.
Final October Counts and Patch Data
The immediate milestone is the completed October tally. Meyer’s 17,000-record figure is an estimate based on the month’s pace through Oct. 25; a final count will show whether publication volume continued at that rate. Further comparison across the NVD, CVE.org and CISA records could help clarify how the disclosure total relates to vulnerabilities catalogued as exploited, though these databases measure different things.
For the AI question, clearer attribution and more consistent reporting would be needed to estimate how often models contribute to finding or validating flaws. Patch progress also requires follow-up: Anthropic’s reported 516 patched vulnerabilities may change as maintainers respond, but the analysis does not give a deadline for a new update. Until those figures and the final October count are available, the confirmed development is a large increase in published CVE records—not a measured increase in AI-discovered bugs or a complete account of the risk to users.
Key Questions
How many CVE records were published in October 2026?
The analysis counted 13,934 records from Oct. 1 through Oct. 25. It says the month’s total could reach about 17,000 if that pace continued, but that is a projection, not a final figure.
Does the increase prove AI found most of the vulnerabilities?
No. The analysis found explicit AI-related credit on 200 October records, or 1.4%, but 54% of records named no finder. The available records therefore cannot measure AI’s overall contribution.
Are more CVE records proof that attacks are increasing?
No. A CVE is a vulnerability disclosure record, not proof that an attacker has exploited the flaw. The analysis cites CISA’s 245 additions to its Known Exploited Vulnerabilities catalog in 2025, but does not provide a matching full-year 2026 total.
What does the analysis say about patching?
It reports that Anthropic had told maintainers about 6,157 vulnerabilities and that 516 were patched to its knowledge. That is information about Anthropic’s reported set, not the patch status of all CVEs.
Source: ThorstenMeyerAI.com